Strategies
Review security responsibilities for a Magento store
Record who handles patching, administrator access, payment integration, alerts and recovery. Outsourcing payment processing leaves responsibilities with the merchant.
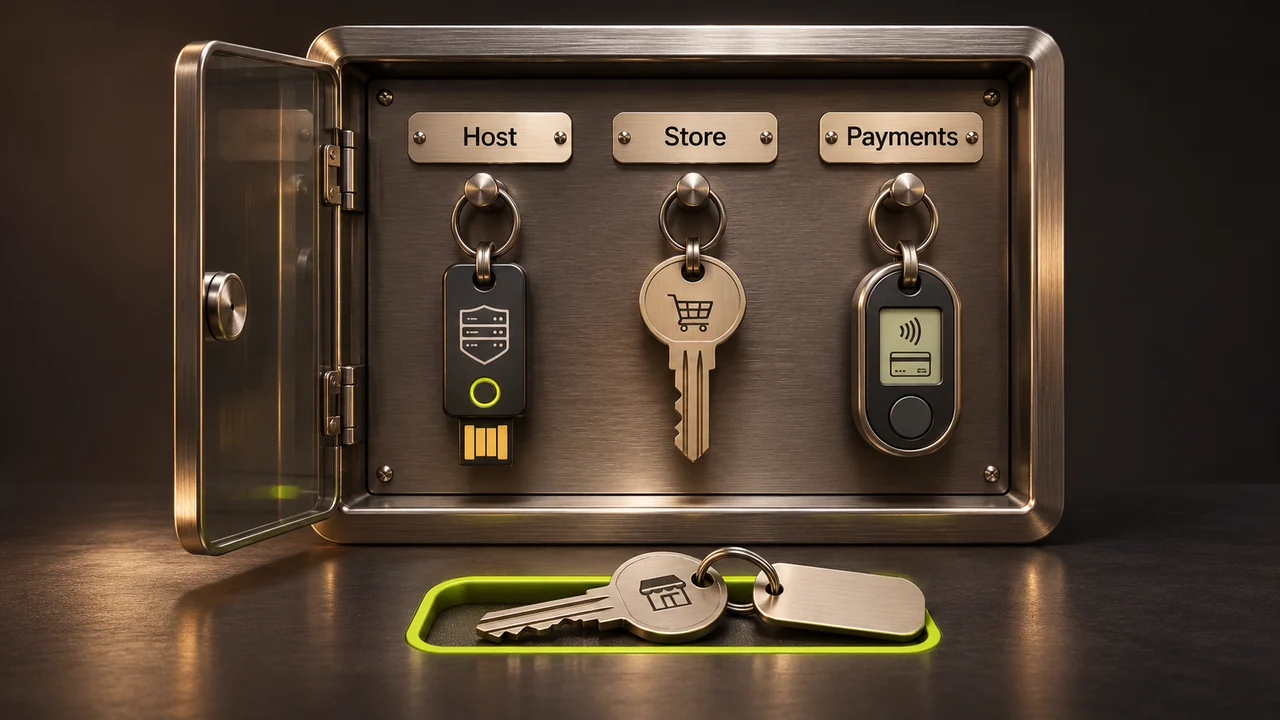
Maintaining a store involves several owners. One team might manage the host, another the Commerce application and a third the payment provider. Record which team is responsible for each control and how they will be contacted.
Maintain a known configuration
Keep a versioned inventory of the application, extensions and integrations. Review support status and vendor updates. Use a staging copy to check catalogue, checkout and administrative tasks before applying a change to production.
Limit access
Give staff individual accounts with only the permissions they need and use multi-factor authentication for administrative access. Review accounts when staff or suppliers change. Keep production credentials out of exports, code repositories and general support messages.
Check the payment boundary
Ask the payment provider which parts of the customer journey it hosts and which remain in your website. Outsourcing payment processing can change applicable PCI DSS responsibilities. It does not automatically establish that the merchant fulfils them. Confirm the arrangement with the provider and the party responsible for your assessment.
Practise recovery
Maintain protected backups and periodically restore an isolated copy. Assign someone to review alerts, contact the host and preserve relevant incident records. Check that changes to access, extensions or hosting also update the recovery instructions.